

How To Integrate AI Into Your Existing Security Program Without Breaking What Works
Liferaft | September 25, 2026
Contents
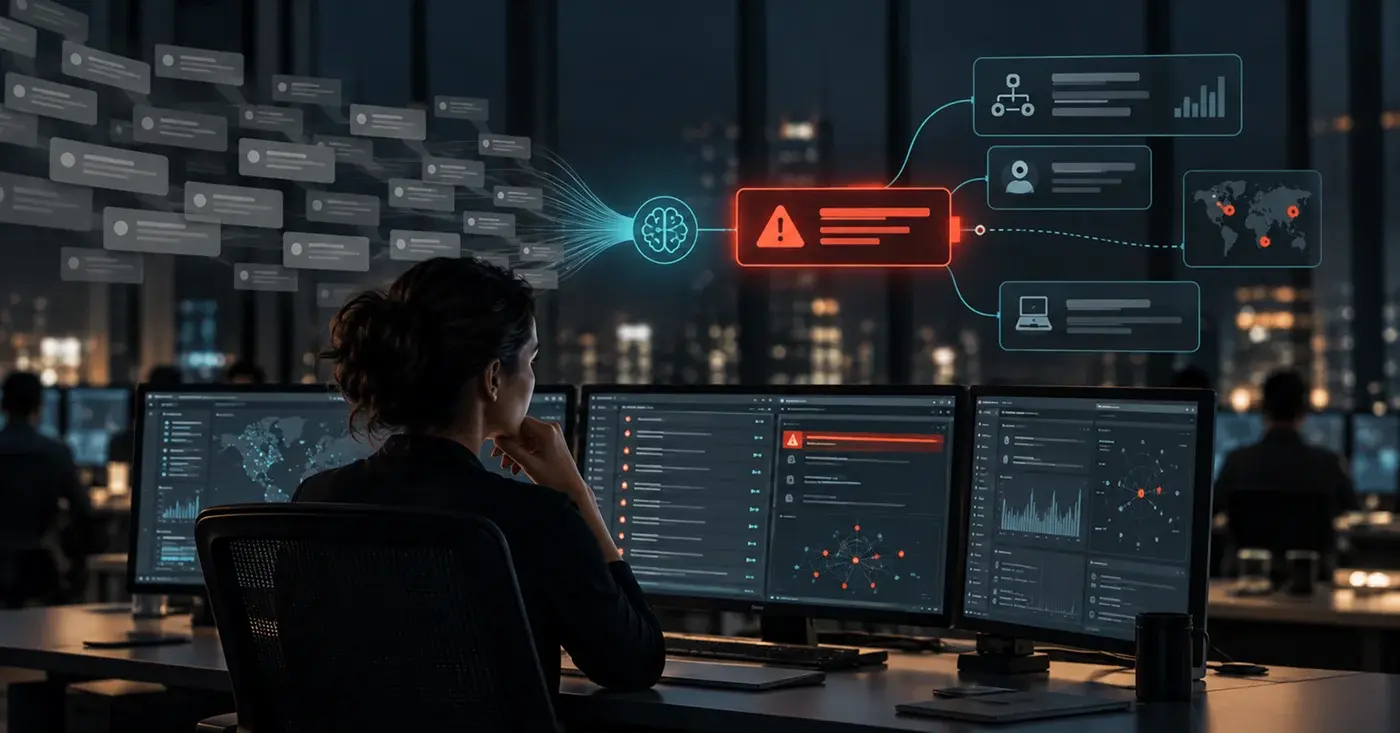
It's 2:40 a.m. and the overnight operator in a GSOC has 380 unread alerts from keyword monitoring. Most of them are harmless. A sports blog mentions the CFO's name because he shares it with a backup quarterback. A local news outlet has republished last week's earnings coverage. Somewhere in that queue, one post from a newly created account references the CEO's upcoming site visit and the parking structure where her car will be. The operator will get to it eventually, after working through the 200 or so alerts that arrived ahead of it.
That queue is the reason most corporate security leaders are looking at AI right now. The promise is faster triage, better prioritization, and more analyst time spent on the alerts that matter. The risk is buying a tool that adds a new console, a new set of alerts, and a new layer of uncertainty to a team that's already stretched. The difference usually comes down to how the integration is planned, and the practices below come from watching security teams get this right and wrong.
Map The Workflow Before You Pick The Tool
Start by documenting what happens today when information enters your program. Where does it come from? Who sees it first? How long does it sit before someone reviews it, and what happens next? Most teams that do this exercise find their time goes to a few specific steps, such as deduplicating mentions, translating foreign-language posts, or checking whether an alert matches something already under review.
Those steps are where AI earns its place. A model that clusters 40 near-identical posts about a product recall into a single item gives an operator back real minutes on every shift. A general promise to 'enhance detection' gives you nothing you can measure, so pick one bottleneck, apply AI there, and measure the change before expanding.
Tie Every Model To Your Collection Requirements
AI tools are very good at sorting information. They need to know what they're sorting for. If your program has written collection requirements and priority intelligence requirements, those become the logic the model uses to decide what gets surfaced first. A post that references a named executive, a specific location, and a date should rank above a post that mentions the company name in passing.
Teams without documented requirements tend to get generic output. The model flags anything with violent language, which means song lyrics, video game chatter, and sports trash talk all land in the queue alongside the one post that deserves attention. Writing requirements first takes a few weeks, but it also makes every tool you buy afterward more useful.
Decide Which Actions Stay With An Analyst
Before rollout, write down which actions the AI can take on its own and which ones require a person. Most mature programs let automation handle deduplication, translation, entity tagging, and initial scoring. Anything that triggers a real-world response stays with an analyst. That includes notifying an executive protection detail, contacting law enforcement, locking down a facility, or opening an investigation into an employee.
This line matters for two reasons. The first is accuracy, since models still misread sarcasm, regional slang, and coded language. The second is accountability. When a CSO briefs the general counsel on why the company acted on a threat, the explanation needs to include a trained person who reviewed the information and made the call.
Look For AI That's Built Into The Workflow
Many security platforms now advertise AI features, and the way those features are built matters more than the label. Some tools add a chatbot or a summary button on top of an older product. An analyst has to leave the task in front of them, open a separate panel, ask a question, and then carry the answer back into their work. That extra step adds time on every alert, and on a busy shift it usually gets skipped.
The strongest platforms put AI at each stage where an analyst already spends time. During collection, it filters out irrelevant matches such as the CFO who shares a name with a backup quarterback. During triage, it scores and clusters alerts so the operator sees one item about a product recall instead of 40. During an investigation, it helps connect an anonymous account to related activity across platforms, and when the case wraps, it drafts a summary the analyst can edit and send to leadership. Each step should happen inside the same platform, with findings flowing into the queue and the case file your team already works from.
Analyst control is the other half of the picture. A well-designed platform shows why it scored an alert the way it did, so an analyst can see which names, locations, or phrases drove the result. Analysts should be able to override a score, dismiss a false positive, and adjust monitoring terms without filing a request with the vendor. Every action that leads to a real-world response should still require a person to approve it.
When AI handles the sorting, and the analyst keeps the decision, the team gets faster without giving up the judgment that makes its work credible.
Challenge Vendors With A Threat You've Already Faced
Every vendor demo looks impressive because the vendor chose the data. A more useful test puts your own experience at the center of the evaluation. Pick a threat your team dealt with in the past few months, such as a post naming an executive, an unlawful protest that formed around one of your facilities, or leaked employee credentials that turned up on a forum. Give the vendor the basic parameters your team had at the start, including the names, locations, and timeframe involved, and ask them to show you what their platform would have surfaced.
Watch for a few specific things during that session. Did the platform find the original post, or only the coverage that followed it? How early would the alert have reached your queue compared with when your team actually learned about it? Did it connect the account behind the post to related activity on other platforms? Could an analyst move the finding straight into a case with the source material attached, or would someone need to copy and paste screenshots into another system?
Settle Governance Before Anyone Asks
Legal, privacy, and HR teams will have questions, and it's easier to answer them before launch. Document what data the tool collects, where it's stored, how long it's retained, and whether the vendor uses your data to train models shared with other customers. If your monitoring touches employees, get HR and legal aligned on scope in writing. Programs that skip this step often find themselves pausing a working tool months later while those conversations finally happen.
Where This Leaves The GSOC
Back at 2:40 a.m., a well-integrated system changes the operator's night in specific ways. The duplicate earnings coverage collapses into one item. The quarterback mentions drop to the bottom. The post about the parking structure sits at the top of the queue with the account's creation date and related activity already attached, and the operator reviews it within minutes of it appearing. Liferaft's Threat Monitoring & Alerting platform was built around that sequence, with AI handling the sorting and analysts making the decisions. If your team is planning its next step with AI, our earlier piece on integrating OSINT into existing security systems covers the groundwork that makes it go smoothly.